Blog tag
Governance, Risk, and Compliance (GRC)
Articles from the SimpleRisk blog tagged Governance, Risk, and Compliance (GRC): governance, risk management, and compliance insights.
France and Italy Tighten Email Tracking Rules: How to Adapt Your Compliance Program
European privacy watchdogs are taking a harder line on digital tracking. If you do business in Italy or France, now's the time to review your use of tracking capabilities across all apps and platforms that generate email.
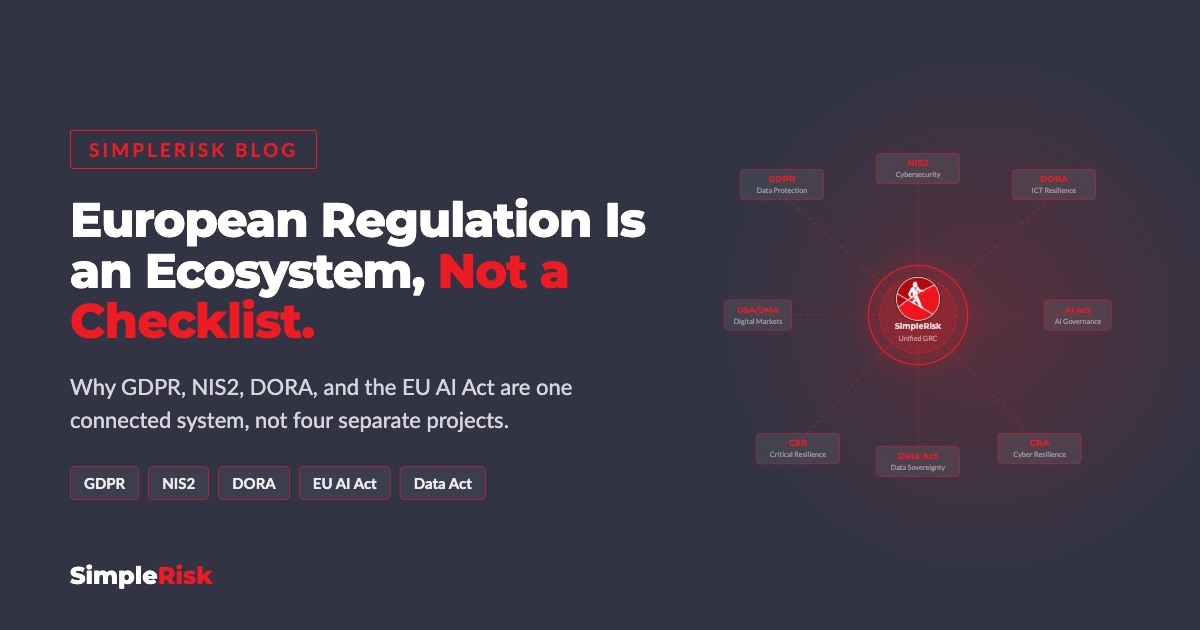
European Regulation Is an Ecosystem, Not a Checklist
GDPR, NIS2, DORA, and the EU AI Act are not separate projects. They overlap on the same data, systems, and vendors, and treating them as one connected system beats a drawer full of checklists.

We're Not Going to Pretend
Every GRC vendor is announcing AI capabilities right now. Here’s what we actually do, what we don’t do, and where we’re going; in plain language.

From Chaos to Control: Centralize Your GRC
If Excel were enough for risk management, the GRC industry wouldn’t exist. Here’s why relying on spreadsheets and generic SaaS tools can actually increase risk, and how centralization restores control.